· Strategy
Agentic Coding Security: Governing AI-Written Code in the SDLC
Agentic coding security starts by treating agent-written code as a supply-chain input: track provenance, scope permissions and keep audit trails.
Agentic coding security starts by treating agent-written code as a supply-chain input: track provenance, scope permissions and keep audit trails.
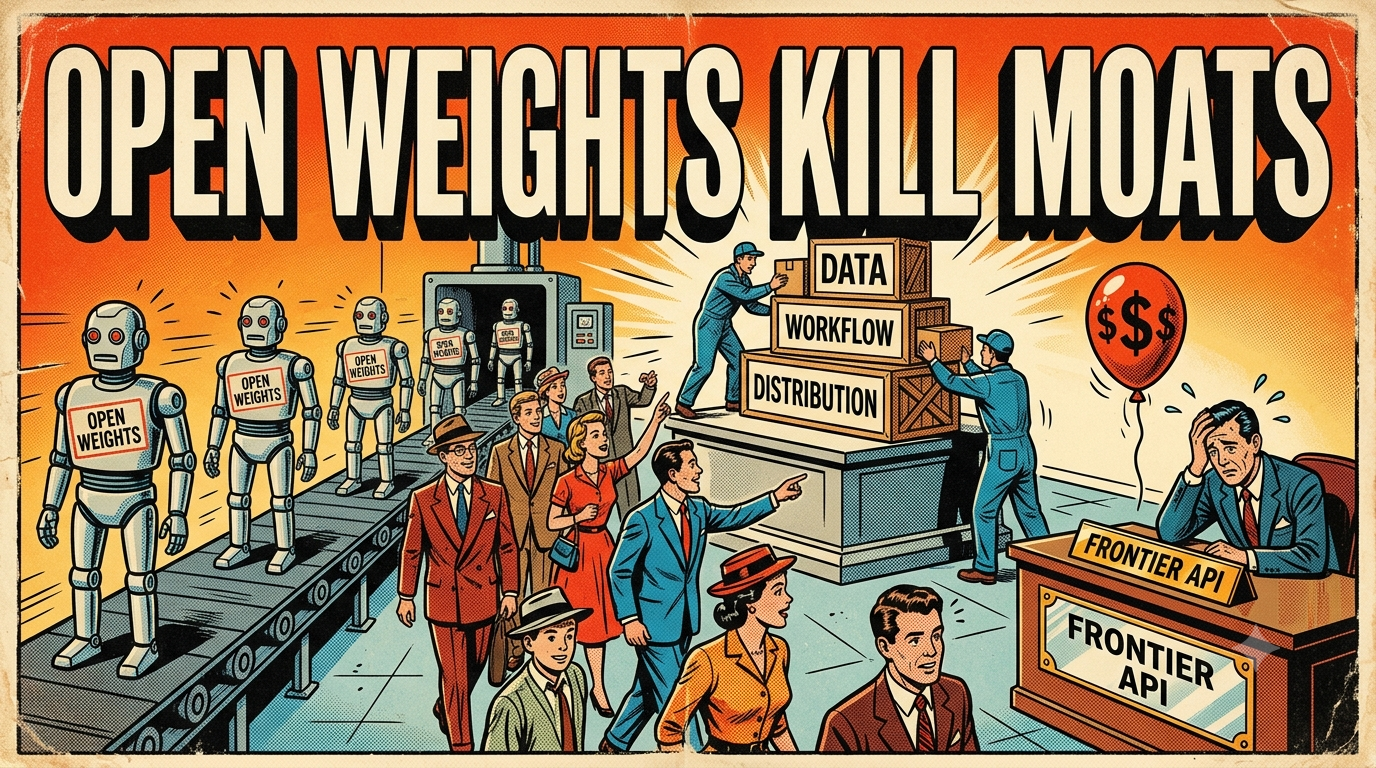
Open weights reshaped the model moat for commodity-tier workloads. The assets that compound are first-party data, workflow ownership, and distribution, not parameter scale. A framework for what to actually protect.
Agents with cloud credentials execute thousands of API calls per minute. Standard billing guardrails built for human interaction break entirely. Here is how to architect cost governance at machine speed.
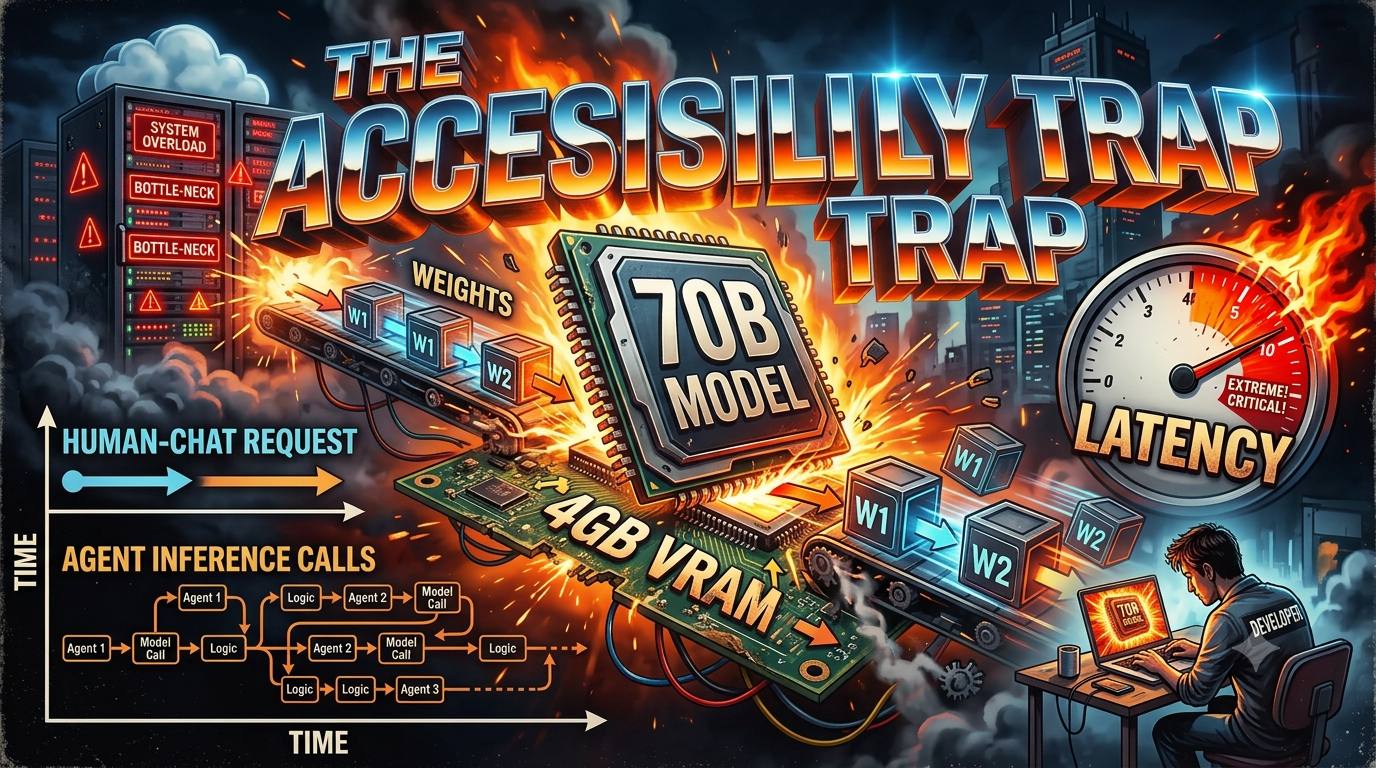
AirLLM runs 70B models on a 4GB GPU. The trick is not the sharding; it is that enterprise inference workloads break the edge cost model. Here is why GPU accessibility is not the same thing as cost efficiency.
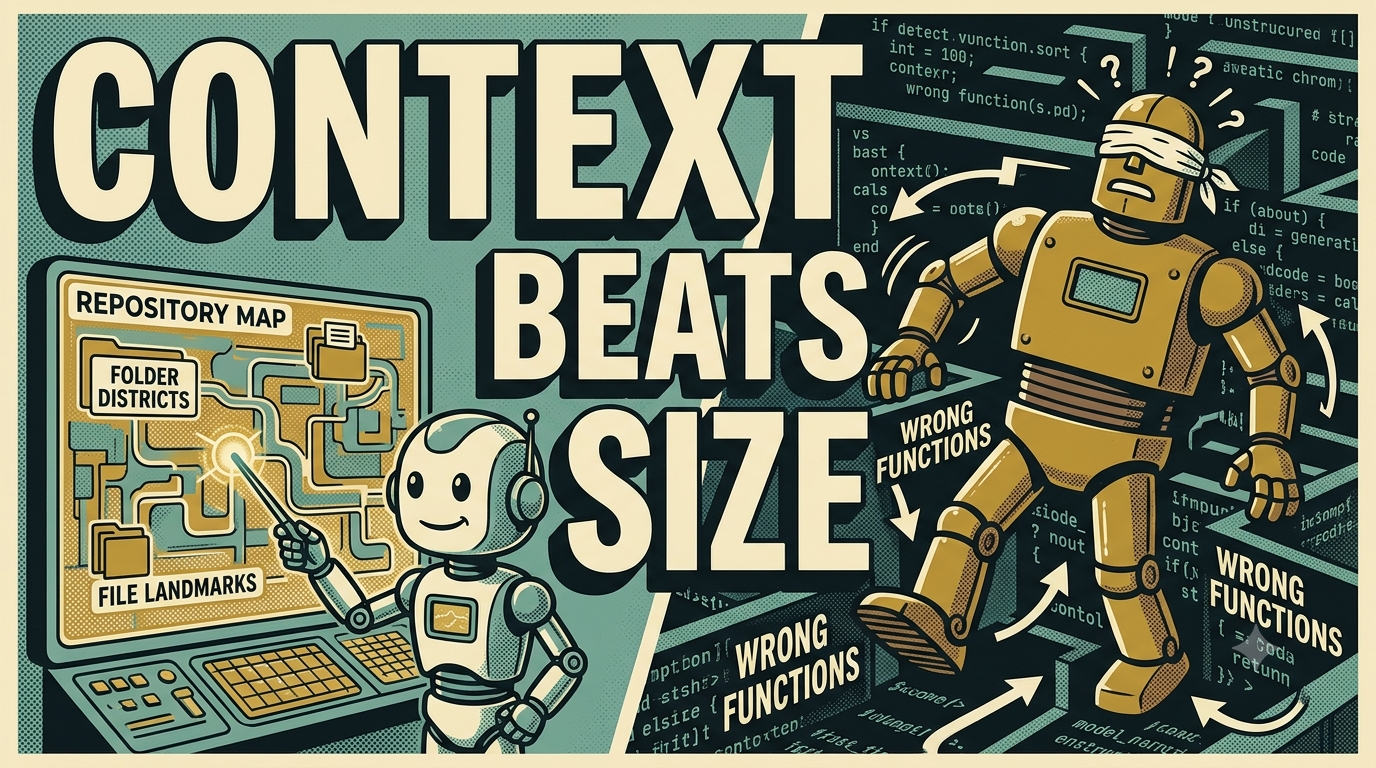
code-review-graph at 20K stars. AI coding agents are moving past generic code search. The next layer is persistent structural indexing through MCP — how agents go from helpful junior to autonomous contributor.
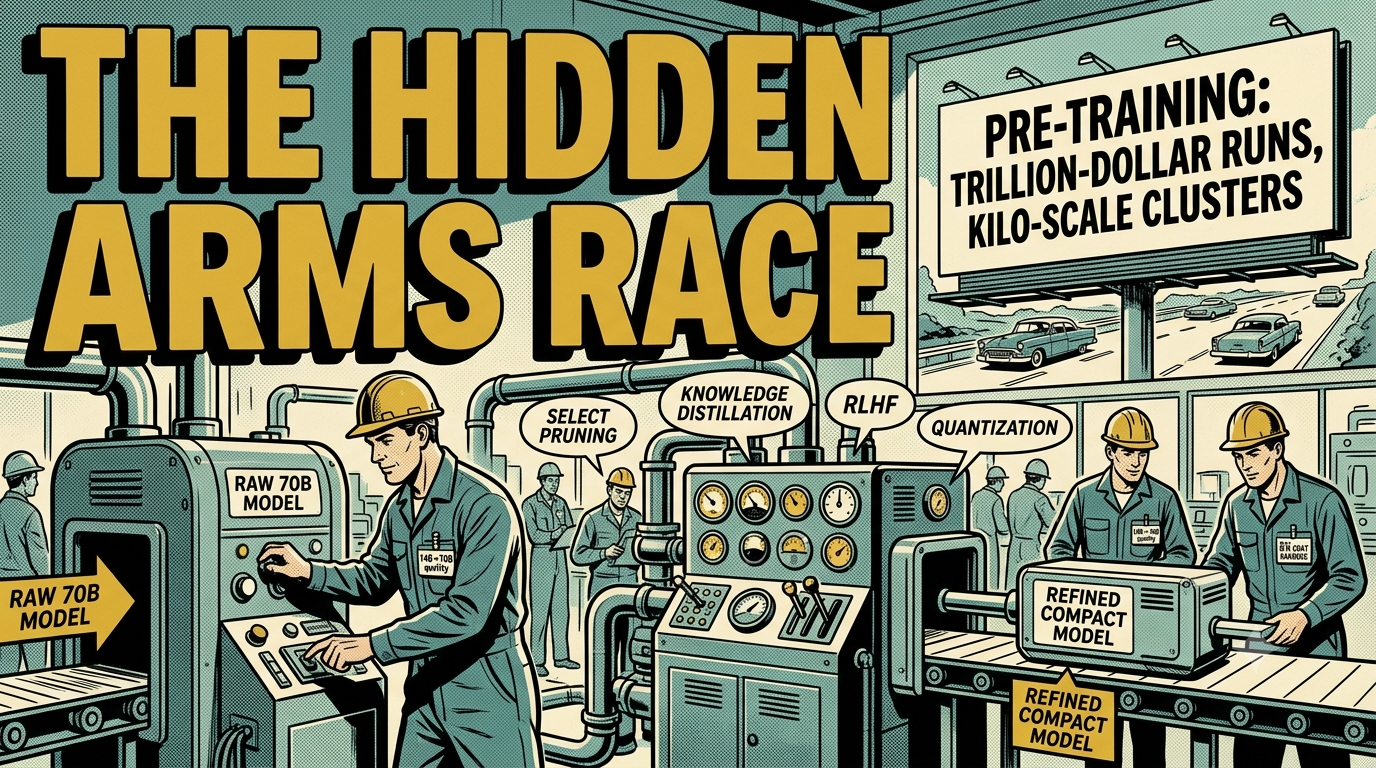
All frontier labs have converged on distillation as their primary post-training method. The real innovation is no longer in pre-training but in post-training pipeline design. Here is why distillation will define competitive advantage in the next AI cycle.